Executive Summary
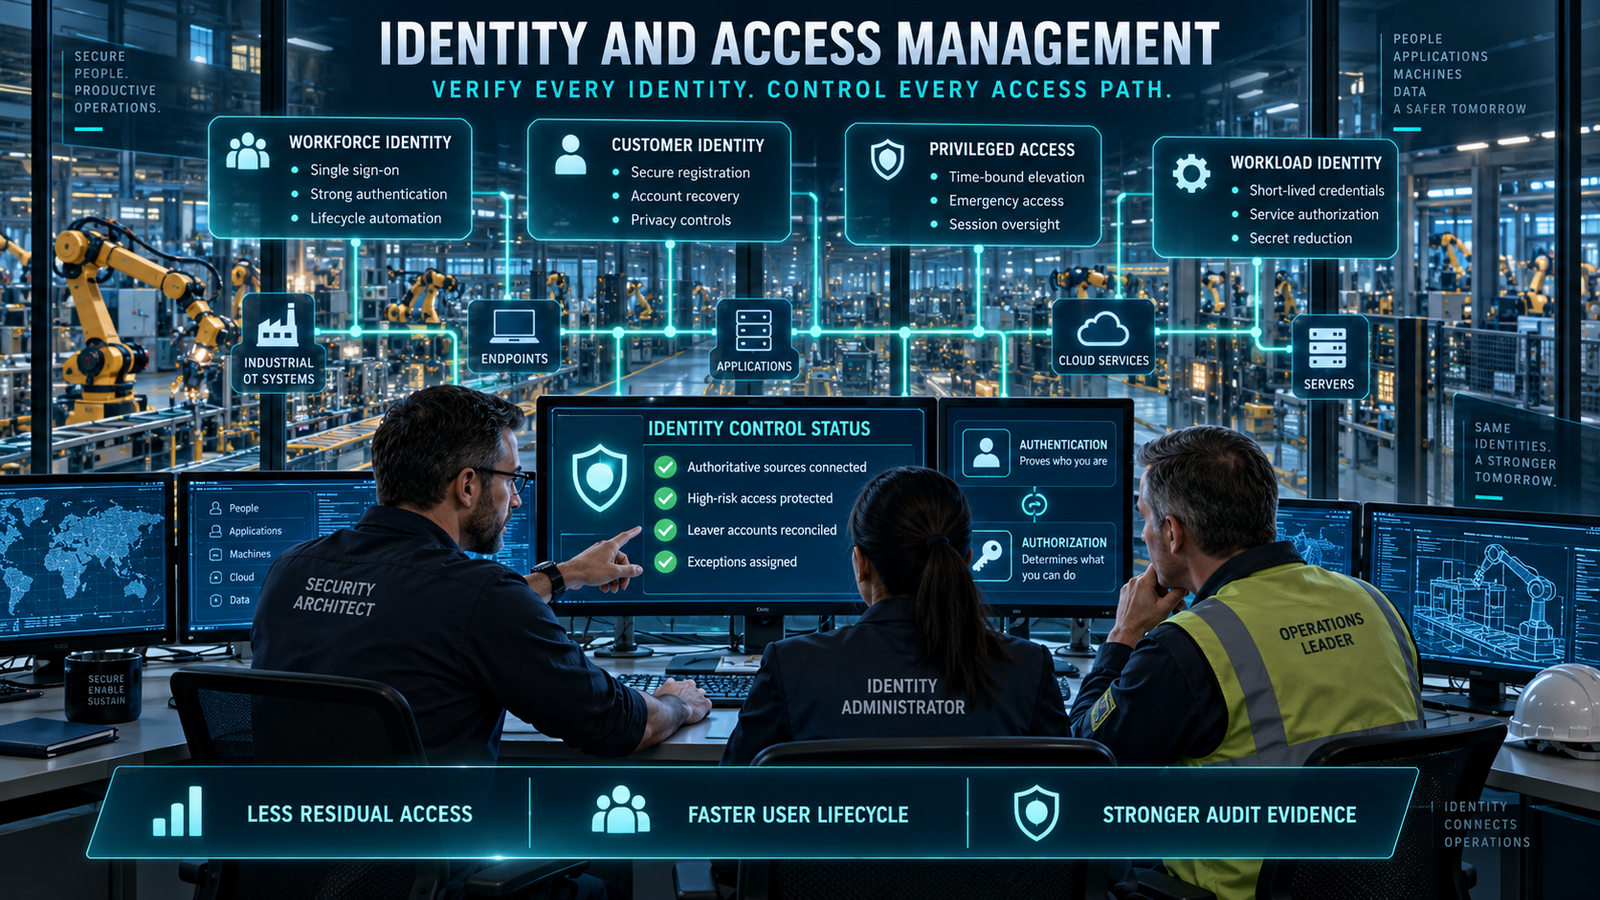
Identity and access management is now an enterprise control plane, not a login convenience. It determines which human or machine identity can reach a resource, under what conditions, with which privileges and for how long.
The buying problem is harder than vendor feature pages suggest. Workforce SSO, customer identity, lifecycle automation, privileged access, entitlement governance and cloud permissions solve different failure modes.
A platform can enforce phishing-resistant authentication yet leave service accounts unmanaged. It can automate onboarding while preserving excessive entitlements inherited through nested groups.
This Article replaces generic IAM definitions with deployment realities. It maps architecture, protocols, lifecycle flows, operating costs, failure vectors, vendor categories, performance measures and regulatory considerations.
The central recommendation is simple. Build the identity model before buying the dashboard, use authoritative sources for lifecycle events and treat recovery paths as security-critical authentication routes.
I. The Current Market Landscape and Challenge
Identity and Access Management Is an Integration Problem
The visible login page is the smallest part of an identity and access management program. The harder work sits behind it: identity correlation, source-of-truth decisions, entitlement models, legacy protocols, non-human credentials and exception handling.
An employee may exist simultaneously in HR, Active Directory, a cloud directory, payroll, customer support and dozens of SaaS tenants. If those records do not share a reliable identity key, automation can provision the wrong person or fail to terminate every account.
Acquisitions make the problem worse. Duplicate email addresses, incompatible naming rules, unmanaged local administrators and conflicting role structures can break otherwise mature identity and access management controls.
The Cost of Identity and Access Management Inaction
Delayed offboarding leaves active credentials behind. Excessive access increases the blast radius of a compromised account, while manual approvals create slow onboarding and inconsistent evidence.
Help-desk cost also matters, but it should not dominate the security case. Password reset savings are irrelevant if account recovery lets an attacker bypass the strongest authenticator.
Weak identity and access management slows customer security reviews and internal audits because ownership, access rationale and revocation evidence must be reconstructed manually. The commercial damage appears as engineering interruption, delayed procurement and avoidable risk acceptance.
Identity and Access Management Must Separate Identity Populations
Four identity populations demand different architecture:
- Workforce identities: employees, contractors and partners accessing corporate resources.
- Customer identities: consumers or business users authenticating to a product.
- Privileged identities: administrators and operators capable of high-impact actions.
- Workload identities: applications, services, devices, agents, containers and automation.
Reusing workforce policies for customers creates friction and privacy problems. Applying consumer registration patterns to administrators can weaken assurance and recovery.
Machine identities are frequently the least governed population. Long-lived API keys, shared secrets, build credentials and cloud roles can bypass human MFA entirely.
Identity and Access Management: Authentication Is Not Authorization
Authentication establishes confidence that a claimant controls an enrolled authenticator. Authorization decides whether the authenticated subject may perform a requested action on a resource.
The distinction is operational, not academic. Strong authentication paired with an overbroad administrator role still produces excessive risk.
NIST SP 800-63-4 separates identity proofing, authentication and federation requirements, while its companion volumes provide detailed technical requirements.[1] The July 2025 edition superseded SP 800-63-3 and should replace outdated password-policy folklore.[1]
II. Deep-Dive Technical Analysis and Evidence
Identity and Access Management Architecture Overview
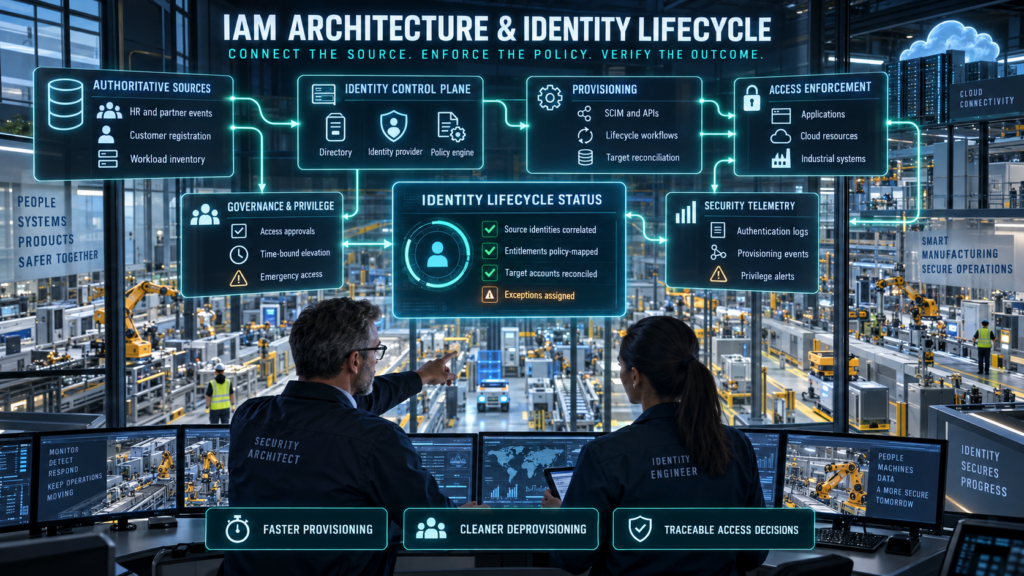
An enterprise architecture needs one authoritative identity lifecycle, even when several directories and applications participate. The HR system may establish workforce status, while the directory governs authentication and downstream applications enforce entitlements.
Core Architecture Components
- Authoritative source: HRIS, partner registry, customer directory or workload inventory.
- Identity provider: authentication, federation, session and policy decision services.
- Directory: identities, groups, attributes, devices and credential references.
- Provisioning layer: SCIM connectors, APIs, workflows and reconciliation jobs.
- Policy engine: role, attribute, device, risk and resource conditions.
- Enforcement points: applications, gateways, databases, cloud control planes and networks.
- Governance layer: requests, approvals, reviews, segregation of duties and evidence.
- Privileged layer: credential vaulting, elevation, session control and emergency access.
- Telemetry layer: sign-in, policy, entitlement, provisioning and administrator events.
Good identity and access management architecture avoids making the identity provider the only source of entitlement truth. Many applications retain local roles that federation alone cannot remove.
Identity and Access Management Integration Flowchart
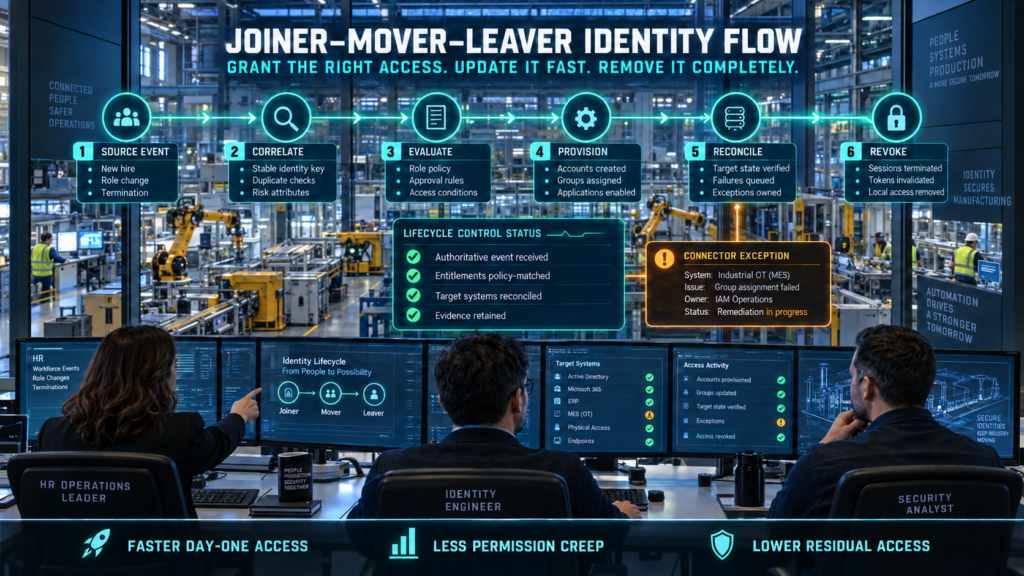
Authoritative HR or partner event
↓
Identity correlation and policy evaluation
↓
Account create, update, suspend or terminate
↓
Application provisioning and entitlement assignment
↓
Reconciliation against target-system state
↓
Exception queue, owner decision and evidence retention
The reconciliation step is essential. An API success response proves a request was accepted; it does not prove the target account reached the intended state.
For leavers, the identity and access management flow must address active sessions, refresh tokens, device certificates, API keys, shared accounts and privileged elevation. Disabling a directory object alone may not invalidate every access path.
Identity and Access Management Federation Protocols
SAML 2.0 is widely used for browser-based enterprise federation. OpenID Connect adds an identity layer over OAuth 2.0 and is commonly used by modern web and mobile applications.
OAuth 2.0 is an authorization framework, not an authentication protocol by itself. Treating an access token as proof of user identity without the appropriate OpenID Connect validation can create security defects.
RFC 9700, published in January 2025, documents OAuth 2.0 security best current practice and deprecates less secure deployment patterns.[5] Architects should validate redirect URIs strictly, use authorization code flow with PKCE where applicable and avoid exposing bearer tokens.
| Standard | Primary function | Typical use | Common implementation failure |
| SAML 2.0 | Federated authentication assertions | Enterprise browser SSO | Weak certificate lifecycle, broad audience, unsigned or poorly validated assertions |
| OpenID Connect | User authentication and identity claims | Modern web, mobile and API ecosystems | Incorrect issuer, nonce, audience or signature validation |
| OAuth 2.0 | Delegated authorization | API access | Using access tokens as identity proof; insecure redirect and token storage |
| SCIM 2.0 | Identity provisioning | SaaS account and group lifecycle | Connector drift, partial deprovisioning and missing reconciliation |
| WebAuthn | Public-key authentication | Passkeys and security keys | Weak recovery, incomplete device coverage and poor enrollment controls |
Passwordless Identity and Access Management Deployment
WebAuthn enables applications to create and use scoped public-key credentials through authenticators.[4] The private key remains protected by the authenticator, while the relying party validates signed challenges.
This design can resist credential replay and phishing when correctly bound to the relying-party origin. “Passwordless” does not remove account recovery, enrollment, device replacement or authenticator lifecycle risk.
Biometrics usually unlock a local authenticator; the server need not receive a fingerprint or face template. Calling any biometric flow phishing-resistant without inspecting the protocol, origin binding and recovery channel is unsafe.
A staged passwordless authentication deployment should cover registration assurance, authenticator inventory, lost-device response, multiple authenticators, high-risk recovery and help-desk verification. Executives should test the fallback path with the same rigor as the primary path.
Identity and Access Management MFA Failure Modes
MFA raises attacker cost, but factors differ materially. SMS codes, push approvals, one-time passwords, device-bound certificates and FIDO credentials do not provide equal phishing resistance.
Attackers can use adversary-in-the-middle pages, push fatigue, SIM-swap fraud, session theft or help-desk manipulation. An identity and access management program should prioritize phishing-resistant methods for administrators, finance, developers and remote access.
Do not repeat a universal “99.9%” prevention claim. Outcome depends on attack type, factor, enrollment, recovery, session handling, legacy authentication and policy coverage.
Identity and Access Management Authorization Models
Role-based access control scales when job functions are stable and roles remain comprehensible. It fails when teams create hundreds of one-off roles or embed temporary exceptions permanently.
Attribute-based access control uses subject, resource, action and environmental attributes. It can express precise policy, but unreliable attributes and inconsistent clocks make decisions hard to debug.
Relationship-based models are useful when access depends on ownership, membership or organizational hierarchy. Whatever the model, policy decisions need explainability, version control, testing and denial-by-default behavior for missing context.
Privileged Identity and Access Management Solutions
Privileged access needs a separate operating layer because administrative actions can bypass ordinary controls. Mature programs minimize standing privilege and use approved, time-bound elevation.
Privileged access management solutions may vault credentials, broker sessions, rotate secrets, record high-risk activity and support emergency access. Session recording adds storage, privacy, monitoring and retention obligations.
Break-glass accounts must remain reachable during an identity-provider outage without becoming an unmonitored bypass. Store them securely, restrict use, alert on every authentication and test them under controlled conditions.
Identity and Access Management Governance
Governance answers why access exists, who approved it and whether it remains appropriate. This is different from the identity provider’s job of authenticating a session.
Access reviews fail when reviewers receive thousands of unexplained entitlements. Group permissions, nested roles and local application rights should be translated into business-relevant decisions.
An effective identity and access management review prioritizes privileged, toxic-combination and sensitive-data access. Low-risk birthright access can use different evidence and cadence.
Workload Identity and Access Management
Workloads cannot complete a phone-based MFA prompt. They require short-lived certificates, workload federation, managed identities, signed tokens or other machine-appropriate credentials.
Long-lived cloud keys in source repositories are an architectural failure, not a training problem. Prefer ephemeral credentials tied to workload context and restrict token audience, lifetime and permissions.
Agentic systems add delegation complexity. The system must distinguish the human principal, the agent, the tool invocation and the downstream resource decision.
Identity and Access Management Performance Evaluation Matrix
Measure identity and access management by control outcomes, not the number of connected applications.
| Measure | Calculation | Interpretation | Failure signal |
| Termination completion | Fully revoked leavers ÷ total leavers | Lifecycle reliability | Local accounts, sessions or tokens remain active |
| Revocation latency | Time from authoritative event to verified denial | Exposure window | Queue delays or failed connectors |
| Privileged standing access | Persistent privileged assignments ÷ total privileged pathways | Least-privilege maturity | Administrators retain broad permanent roles |
| Phishing-resistant coverage | Protected in-scope identities ÷ targeted identities | Strong-authentication reach | High-risk users remain on weaker factors |
| Provisioning reconciliation | Matched target accounts ÷ expected accounts | Connector accuracy | Orphans, duplicates or mismatched entitlements |
| Access-review decision quality | Actionable removals and validated approvals ÷ reviewed items | Review usefulness | Blanket approval and reviewer fatigue |
| Recovery-path assurance | Tested recovery routes ÷ in-scope recovery routes | Bypass resistance | Help desk or fallback factor is weaker than primary login |
| Workload credential age | Credential age by risk tier | Secret lifecycle | Long-lived keys with unknown owners |
Set targets from system criticality and policy, not arbitrary industry averages. A single enterprise-wide average can hide high-risk administrators behind thousands of ordinary users.
Identity and Access Management Deployment Challenges
Legacy Identity and Access Management Applications
Legacy systems may lack SAML, OIDC or SCIM support. Header-based gateways and password vaulting can bridge the gap, but they add availability dependencies and may not control local authorization.
Do not mark an application complete when SSO is enabled. Verify local accounts, administrator paths, session invalidation and deprovisioning.
Multi-Cloud Identity and Access Management
Cloud platforms expose different role, policy and resource models. A central identity and access management layer can federate authentication while cloud-native authorization still creates excessive permissions.
Cloud infrastructure entitlement management (CIEM) helps identify excessive, unused or risky cloud permissions. Remediation must account for workload dependencies, including scheduled jobs and disaster-recovery procedures. A permission that appears unused during routine monitoring may still support an essential recovery operation.
Identity and Access Management Outages and Concentration Risk
Centralization simplifies policy and creates concentration risk. If the identity provider fails, employees may lose access to communication, incident tooling and production recovery systems simultaneously.
Architect offline and emergency paths for critical operations. Test failover, cached sessions, certificate dependencies, DNS, time synchronization and administrator recovery.
Identity and Access Management Correlation Errors
Matching identities only by email address can merge or split records incorrectly after name changes, acquisitions or account reuse. Use stable identifiers and define manual review for ambiguous matches.
A bad joiner record can grant access to the wrong person at machine speed. Automation needs validation, separation of duties and rollback.
Guest Identity and Access Management
External users often outlive their sponsor or project. Require an accountable sponsor, expiry, periodic recertification and a clear termination event.
Federated guests can retain access even after the partner changes employment status. Cross-tenant identity and access management needs both home-organization signals and resource-owner review.
Customer Identity and Access Management at Scale
Customer identity platforms must handle registration abuse, account recovery, consent, fraud, privacy and traffic spikes. Workforce directories are rarely designed for those product requirements.
Rate limiting and bot detection reduce abuse but may block legitimate users. Accessibility, regional data handling and recovery support need equal consideration.
III. Commercial Solutions and Best Practices
Identity and Access Management Feature and Cost Comparison Table
The following comparison uses vendor-owned public information reviewed for this paper.[9][10][11][12] Capabilities, bundles and prices change; obtain a written quote and bill of materials before purchase.
| Platform | Primary fit | Publicly emphasized strengths | Pricing visibility | Key limitation to test |
| Microsoft Entra | Microsoft-centric workforce, cloud access and governance | SSO, conditional access, identity protection, governance and workload identity portfolio | Public plan pricing exists for some components; bundles vary | Licensing dependencies, tenant complexity and non-Microsoft depth |
| Okta Workforce Identity | Heterogeneous SaaS workforce environments | Broad integrations, SSO, MFA, lifecycle and governance options | Module-level list prices and contact-sales packaging | Add-on accumulation, lifecycle connector fidelity and recovery policy |
| Ping Identity | Large hybrid enterprises and complex customer/workforce federation | Flexible federation, orchestration, hybrid deployment and customer identity | Quote-led for many enterprise configurations | Implementation complexity, specialist skills and complete cost model |
| JumpCloud | Small and midsize organizations seeking directory, device and access convergence | Cloud directory, SSO, MFA, device and user management bundles | Public package guidance with sales confirmation | Depth for complex governance, PAM and large regulated environments |
This is not a ranking. The best identity and access management platform is the one that fits the identity population, architecture, assurance requirement and operating capacity.
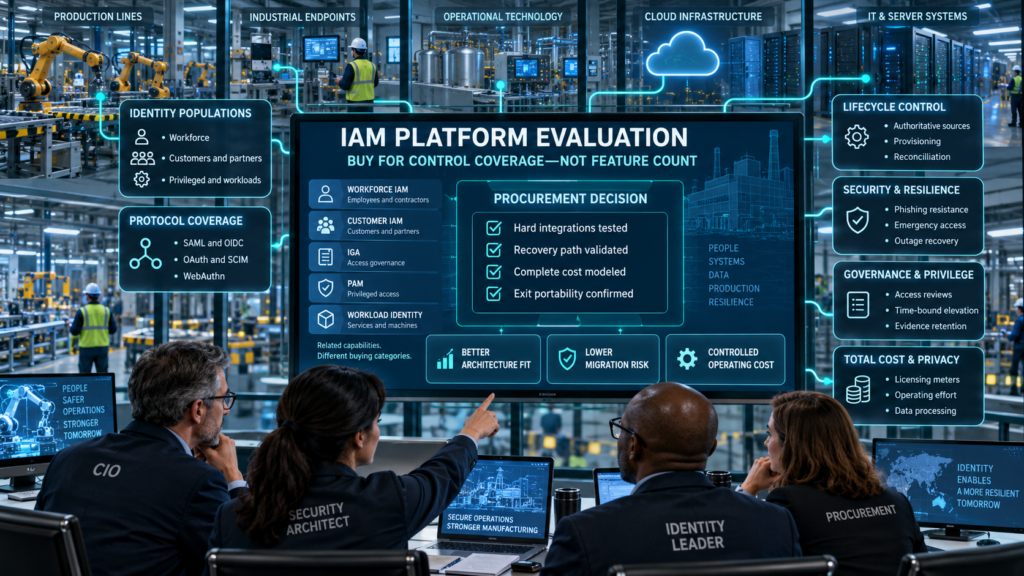
Identity and Access Management Categories Before Products
Workforce IAM handles employee authentication and application access. Customer IAM prioritizes product-scale registration, login, fraud and privacy.
IGA manages access requests, reviews and policy conflicts. PAM governs administrators, elevation, secrets and sensitive sessions.
Directory, device management and cloud-permission products overlap with these categories but do not replace all of them. A vendor suite may integrate the layers; it does not eliminate architectural boundaries.
Identity and Access Management Total Cost of Ownership
Calculate first-year cost as:
Licenses + implementation + connector engineering + migration + support + security keys + change management + internal operations + decommissioning.
Then model renewal cost by active user, monthly active user, application, connection, privileged account, machine identity or governance module. Vendor meters differ and can change the comparison materially.
Open-source software removes some license fees but not infrastructure, patching, on-call support, upgrade testing or security expertise. Managed software transfers operational work, not accountability.
Twelve-Gate Identity and Access Management Procurement Framework
- Population: workforce, customer, privileged, partner and workload identities.
- Protocols: SAML, OIDC, OAuth, SCIM, LDAP, RADIUS, WebAuthn and certificate needs.
- Lifecycle: authoritative sources, correlation, provisioning and reconciliation.
- Authentication: phishing resistance, device binding, policy and recovery.
- Authorization: role, attribute, relationship and application-local controls.
- Governance: requests, approvals, reviews, segregation of duties and evidence.
- Privilege: elevation, vaulting, session control, secrets and emergency access.
- Telemetry: log detail, export, latency, retention and investigation workflow.
- Resilience: regional design, outage behavior, break-glass and recovery testing.
- Privacy: profiling, biometrics, consent, retention and cross-border processing.
- Economics: every meter, add-on, service fee, renewal and exit cost.
- Portability: standards support, export, migration and dependency reduction.
Require a proof of concept using the hardest systems, not only polished SaaS integrations. Include one legacy application, one privileged path, one workload identity and one failure scenario.
Deployment Roadmap
Phase 1: Discover and Stabilize
- Inventory identity stores, applications, privileges, service accounts and recovery paths.
- Define authoritative sources and stable identifiers.
- Remove shared administration and protect emergency accounts.
- Establish log export before changing access paths.
Phase 2: Federate and Strengthen Authentication
- Move suitable applications to SAML or OIDC.
- Disable legacy authentication where operationally safe.
- Deploy phishing-resistant MFA to high-risk populations.
- Test registration, device loss and recovery.
Phase 3: Automate Lifecycle
- Connect HR and partner events to provisioning workflows.
- Implement SCIM or APIs with reconciliation.
- Validate joiner, mover, leaver and rehire scenarios.
- Track failures in an owned exception queue.
Phase 4: Govern Privilege and Entitlements
- Remove standing privilege where time-bound elevation is feasible.
- Introduce risk-based access reviews and toxic-combination rules.
- Rotate or federate workload credentials.
- Measure revocation and reconciliation outcomes.
The roadmap is not a fixed ninety-day guarantee. Application count, legacy integration, organizational change, assurance level and migration risk determine timing.
Identity and Access Management Implementation Checklist
Governance and Scope
- Define accountable executives, service owners and policy owners.
- Separate workforce, customer, partner, privileged and workload populations.
- Record applicable legal, contractual and assurance obligations.
- Establish risk tiers for resources and identity types.
- Approve exception and risk-acceptance authorities.
Identity Lifecycle
- Declare authoritative sources and stable identity keys.
- Map joiner, mover, leaver, contractor and rehire events.
- Reconcile expected access with target-system state.
- Revoke sessions, tokens, credentials and local accounts during termination.
- Assign owners and expiry to guests and contractors.
Authentication and Recovery
- Select assurance requirements by transaction and resource risk.
- Prioritize phishing-resistant authentication for high-risk users.
- Disable weak legacy authentication where dependencies permit.
- Inventory authenticators and support secure replacement.
- Test account recovery and help-desk verification against social engineering.
Authorization and Governance
- Define roles and attributes using business meaning.
- Detect nested-group and inherited-access effects.
- Review privileged and sensitive access at risk-based intervals.
- Enforce segregation of duties where required.
- Preserve approval, review, revocation and exception evidence.
Privileged and Workload Access
- Inventory administrator paths, local accounts and emergency identities.
- Use time-bound elevation when operationally feasible.
- Rotate or eliminate long-lived secrets.
- Restrict token audience, lifetime and permissions.
- Monitor every emergency-access use.
Monitoring and Resilience
- Export authentication, policy, provisioning and administrator logs.
- Alert on risky enrollment, factor reset and privilege change.
- Test identity-provider outage and recovery procedures.
- Validate DNS, certificate, time and network dependencies.
- Measure revocation latency and connector failures.
IV. Business Outcomes and Strategic ROI Takeaways
Model ROI Without Vendor Arithmetic
Do not claim a universal breach reduction or payback period. Identity and access management value depends on baseline maturity, integration scope, labor cost, incident history and business dependence on authentication.
Calculate benefits and costs over the same annual period:
Annual gross benefit = retired-tool savings + realized administration savings + realized access-review savings + recovered license savings + estimated reduction in expected incident losses.
Annual net benefit = annual gross benefit − annual program cost.
Annual ROI (%) = (annual net benefit ÷ annual program cost) × 100.
Document the baseline, source, owner and assumptions for every estimate. Separate realized financial savings from staff time released for other work and modeled incident-risk reduction. Avoid counting the same administrative hours twice. Include implementation and migration costs in the first-year calculation, and calculate recurring-year costs separately.
Cost Optimization Opportunities
Lifecycle automation can remove unused SaaS access after termination or role change. Savings require license-assignment and billing data, not merely an inactive-account count.
Consolidating authentication can reduce duplicated tools, but suite discounts may increase vendor concentration and exit cost. Model both operating simplification and control-plane dependency.
Executive Measures
Executives need exposure measures, not login volume:
- Terminated users with residual access.
- Permanent privileged assignments.
- High-risk users without phishing-resistant authentication.
- Unowned workload credentials.
- Failed provisioning or reconciliation jobs.
- Overdue guest sponsorship reviews.
- Untested recovery routes.
- Critical applications outside centralized policy.
A mature identity and access management dashboard shows exceptions and owners. An all-green score built from incomplete application coverage is worse than an honest amber status.
Risk Mitigation and Regulatory Framework
Failure-Mode Register
| Failure vector | Impact | Mitigation | Evidence |
| Wrong authoritative identity matched | Access granted to wrong subject | Stable identifiers, collision review and reconciliation | Match log, approval and target-state result |
| IdP outage blocks responders | Recovery delay | Tested emergency accounts and offline runbook | Exercise record and alert history |
| MFA recovery uses weak help-desk proofing | Account takeover | Risk-tiered recovery and staff verification controls | Recovery test and support audit trail |
| SSO enabled but local admin remains | Policy bypass | Local-account inventory and disabled fallback | Application configuration and login test |
| OAuth token validated incorrectly | Unauthorized API access | RFC 9700 practices and correct issuer, audience and signature validation | Security tests and configuration review |
| SCIM request succeeds but account persists | Residual access | Target-state reconciliation | Connector log and application export |
| Service key never expires | Long attacker persistence | Workload federation or short-lived credential rotation | Credential inventory and issuance logs |
| Access review receives opaque entitlements | Rubber-stamp approval | Business-readable context and risk prioritization | Review decisions and removal records |
Standards and Regulatory Checklist
- Use NIST SP 800-63-4 for current identity proofing, authentication and federation guidance where applicable.[1]
- Use NIST SP 800-207 to design zero trust around users, assets and resources without granting trust based only on network location.[2]
- Map program outcomes to NIST CSF 2.0 Govern, Protect, Detect, Respond and Recover functions where useful.[3]
- Apply WebAuthn requirements for public-key credentials and verify relying-party implementation details.[4]
- Apply RFC 9700 OAuth security best current practice to modern authorization deployments.[5]
- Evaluate CISA zero-trust maturity guidance without treating maturity stages as certification.[6]
- Determine GDPR, state privacy, sector and employee-monitoring obligations from actual processing and jurisdiction.[7]
- Assess EU AI Act relevance only when IAM risk engines or biometric systems meet the regulation’s factual scope.[8]
- Complete a data-protection impact assessment where required for high-risk biometric or behavioral processing.
- Obtain qualified legal advice for regulatory interpretation.
Privacy, Recovery and Access Limitations
Risk-based access systems can produce false positives, lock out legitimate users and create opaque decisions. Device, location and behavioral signals can also raise workforce privacy and discrimination concerns.
Passkeys improve resistance to credential phishing, but synchronization, recovery and platform dependency still need governance. Identity and access management should never be sold as a guarantee that account takeover is impossible.
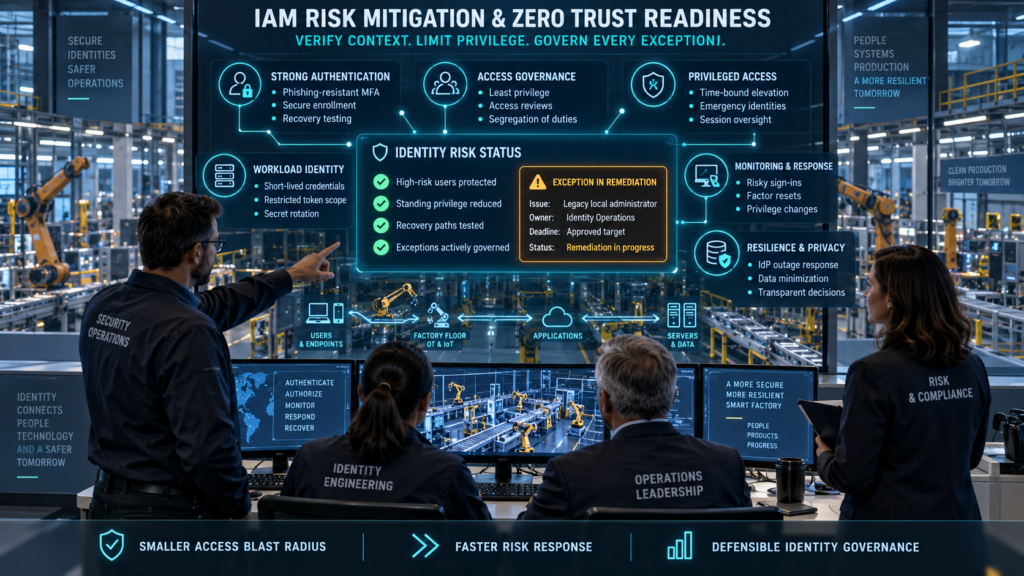
Choosing IAM Tools for Your Highest-Risk Access Paths
Begin with your most business-critical applications and access paths. Map identity sources, administrator privileges, workload credentials and account-recovery procedures. Identify where onboarding, access changes or offboarding leave permissions that should have been removed.
Use those findings to define a focused proof of concept. Test a legacy application, privileged access, workload authentication and an identity-provider outage. Record the owner, acceptance criteria, dependencies and cost of each proposed improvement before selecting a platform.
V. Appendix and Research Integrity
Appendix A: Sources and Reference Links
- NIST, Digital Identity Guidelines, SP 800-63-4. Final July 2025 guidance covering identity proofing, authentication, federation, enrollment, authenticators and lifecycle processes; supersedes SP 800-63-3. https://doi.org/10.6028/NIST.SP.800-63-4
- NIST, Zero Trust Architecture, SP 800-207. Primary architectural source establishing that trust is not granted solely from network location or asset ownership and that authorization protects resources. August 2020. https://doi.org/10.6028/NIST.SP.800-207
- NIST, Cybersecurity Framework 2.0, CSWP 29. Primary risk-management framework organized around Govern, Identify, Protect, Detect, Respond and Recover. February 2024. https://doi.org/10.6028/NIST.CSWP.29
- W3C, Web Authentication: An API for Accessing Public Key Credentials—Level 3. W3C Recommendation defining scoped public-key credentials and authenticator interaction for strong user authentication. August 25, 2026. https://www.w3.org/TR/webauthn-3/
- IETF, Best Current Practice for OAuth 2.0 Security, RFC 9700. IETF Best Current Practice, published as BCP 240, updating OAuth 2.0 security guidance and deprecating insecure deployment patterns. January 2025. https://www.rfc-editor.org/rfc/rfc9700
- CISA, Zero Trust Maturity Model, Version 2.0. U.S. government maturity guidance covering identity, devices, networks, applications/workloads and data. April 2023. https://www.cisa.gov/resources-tools/resources/zero-trust-maturity-model
Regulatory and Commercial Sources
- European Union, General Data Protection Regulation, Regulation (EU) 2016/679. Primary legal text relevant to identity, authentication, monitoring and biometric-data processing where territorial and material scope apply. https://eur-lex.europa.eu/eli/reg/2016/679/oj
- European Union, Artificial Intelligence Act, Regulation (EU) 2024/1689. Primary legal text used to qualify potential duties involving covered biometric or AI-based identity systems; applicability is fact-specific. https://eur-lex.europa.eu/eli/reg/2024/1689/oj
- Microsoft, Microsoft Entra Plans and Pricing. Vendor primary source for public packaging, capabilities and available price information; not independent validation. Accessed September 19, 2026. https://www.microsoft.com/en-us/security/business/microsoft-entra-pricing
- Okta, Plans and Pricing. Vendor primary source for Workforce Identity module descriptions and public pricing information; buyers should confirm scope and current quotes. Accessed September 19, 2026. https://www.okta.com/pricing/
- Ping Identity, Pricing. Vendor primary source for product packaging and sales-led pricing. Accessed September 19, 2026. https://www.pingidentity.com/en/pricing.html
- JumpCloud, Pricing. Vendor primary source for cloud-directory and device/access package information. Accessed September 19, 2026. https://www.jumpcloud.com/pricing
Technical Reference Notes
NIST SP 800-63-4 and SP 800-207 are technical government publications rather than peer-reviewed journal articles. WebAuthn Level 3 and RFC 9700 are consensus standards used because protocol implementation, not a generic survey statistic, determines the relevant engineering claims.
During procurement and ongoing maintenance, review vulnerabilities affecting the specific products, versions and integrations in use. Consult vendor security advisories, the NIST National Vulnerability Database and CISA’s Known Exploited Vulnerabilities Catalog, then prioritize remediation according to exposure and business impact.
Source and Citation Index
| Citation | Claims supported | Article location |
| [1] | Digital identity, authentication and federation guidance | Authentication; architecture; regulatory checklist |
| [2] | Zero trust principles and resource-centric access | Market analysis; regulatory checklist |
| [3] | Cybersecurity lifecycle outcomes | Regulatory checklist |
| [4] | Public-key credentials and WebAuthn | Passwordless deployment |
| [5] | OAuth security best current practice | Protocols; failure-mode register |
| [6] | Zero-trust maturity guidance | Regulatory checklist |
| [7] | GDPR processing and biometric considerations | Privacy and regulatory analysis |
| [8] | EU AI Act scope qualification | Regulatory analysis |
| [9]–[12] | Vendor-described capabilities, packages and pricing routes | Feature and Cost Comparison Table |
Editorial and Commercial Disclosure
AI-assisted tools were used to support research organization, drafting and language refinement. NezzHub retains editorial responsibility for the published article. Vendor inclusion does not constitute endorsement.
No vendor paid for placement. Vendor-owned pages support only attributed product and pricing descriptions, not independent security or performance conclusions.
The paper does not guarantee regulatory compliance, breach prevention, audit results, authentication availability, cost savings or vendor performance. Standards, laws, prices and capabilities can change.
Author and Editorial Review
Author: Garikapati Bullivenkaiah
Technology research writer with LL.B., LL.M., M.A., and MBA qualifications. He writes about emerging technologies and their business, governance and legal implications. His multidisciplinary academic background informs his analysis of technology adoption, intellectual property, and organizational risk. His articles explain technical concepts and practical considerations for business owners, IT managers and technology decision-makers. LinkedIn Profile
Reviewed by: Chitikineni Ramadevi — Editor
Chitikineni Ramadevi holds an M.Sc. in Computers from Andhra University and has over 10 years of research experience in technology-related subjects. She reviews NezzHub articles for clarity, factual accuracy, source support and practical relevance.
Published by: NezzHub
Research approach: This article draws on primary sources, technical documentation and relevant industry research. References are provided within the article or its sources section.
Last reviewed: 09-19-2026
Corrections: To report a factual error or outdated information, please contact NezzHub.